Admins
Admins lists level 0 users and provides authenticated views of identity and account actions.
The /users/admins route requires level 0. The Users sidebar also excludes read-only account types. Route or menu visibility does not grant API permission.
Administrator list
- The page fixes the list filter to Administrator (level 0).
- Query state can include active state, pagination, identity/contact search, and additional filters.
- Selecting a row can request profile and related account data.
Read and privacy boundary
Administrator records can include names, contact details, addresses, birth dates, photos, verification state, order counts, enabled state, wallets, and push tokens. These are private account data; open only records needed for an authorized task and do not assume that a GET request has no side effects.
The general detail menu can expose:
- Profile
- Saved places
- Orders
The panel does not provide the Business owner Businesses tab. It can expose Push tokens when its project condition is met and School students when the school module is enabled.
Persistent action boundaries
The list and detail enabled-state controls submit an immediate user update. Confirmation UI does not make the operation safe or prove the resulting access state.
API source can reject protected-user changes. It also restricts self-level change and administrator deletion, and can block deletion through project configuration.
Profile, credential, and session boundary
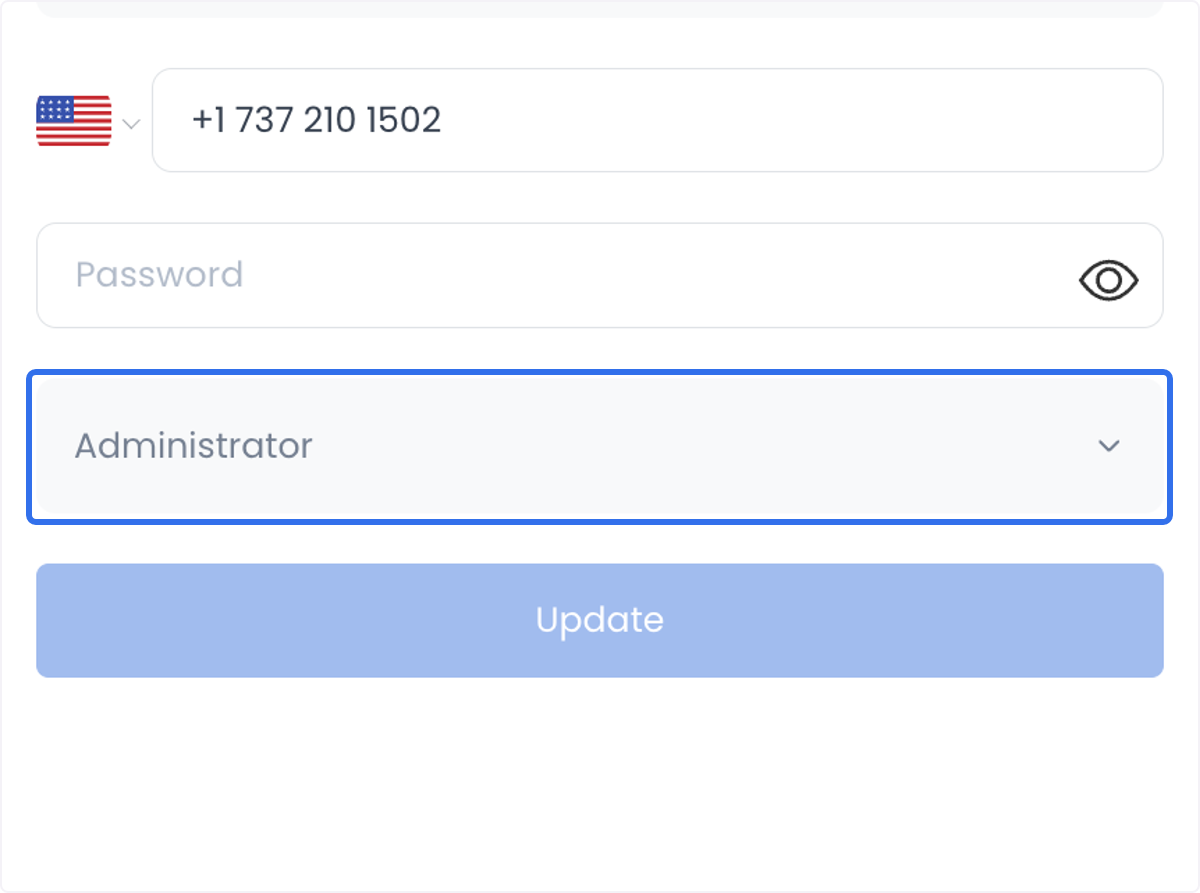
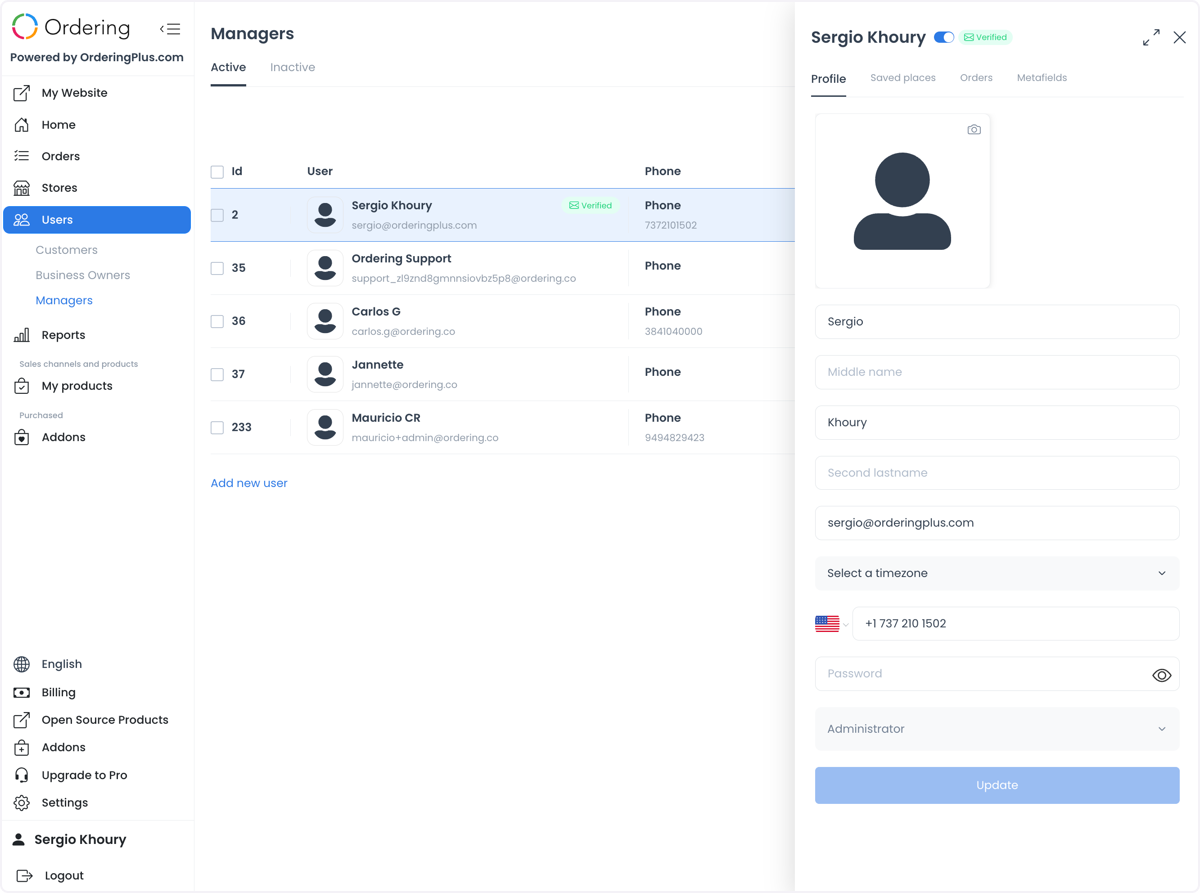
The shared editor can expose configuration-driven profile, contact, timezone, password, image, enabled-state, and role fields. API source validates identity changes; password updates can alter session strategy and revoke other stored sessions. No values or sessions were inspected and no update was sent.
Deletion and disclosure boundary
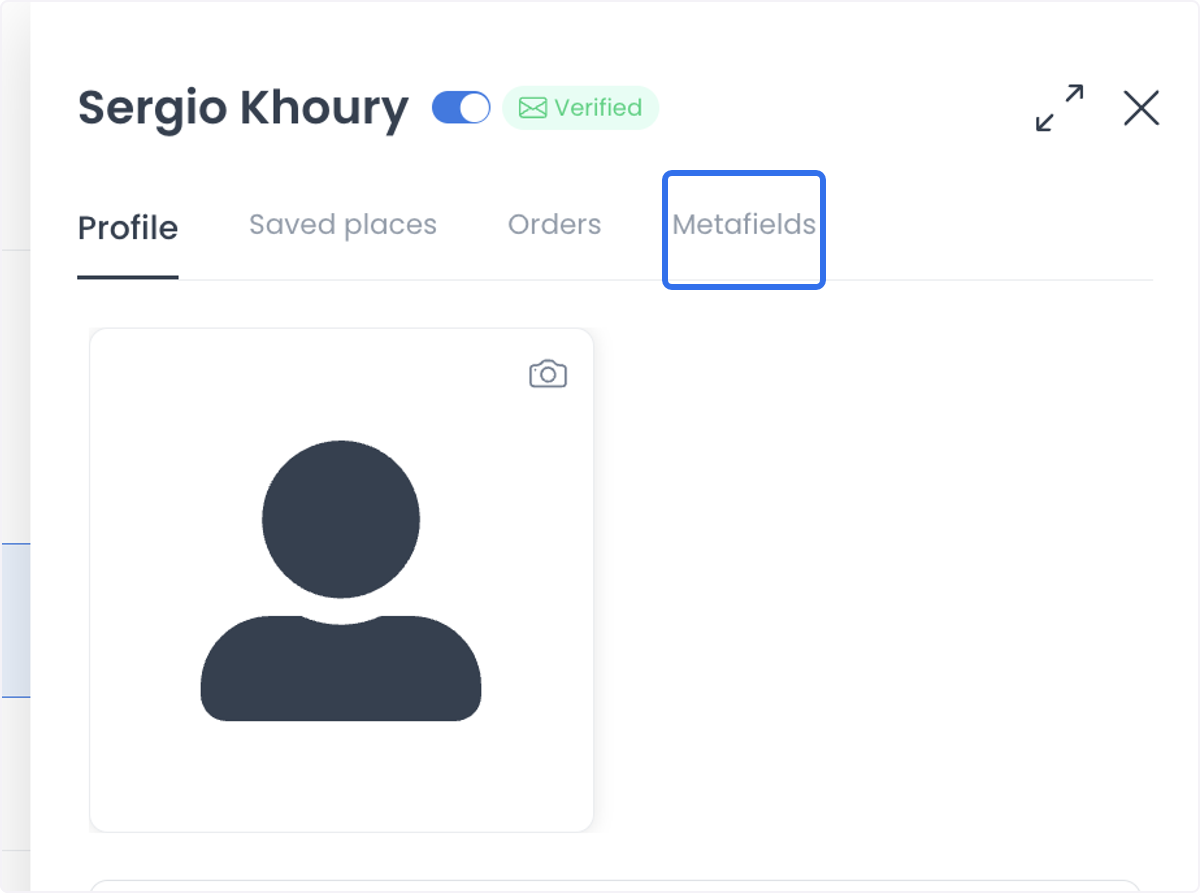
The detail panel can offer Custom fields and may omit Delete for the signed-in Administrator. The list can also provide export and bulk-delete actions. Deletion may change stored identity fields before soft deletion, and exports can disclose personal data. Use these actions only with the required administrative authorization.
Review the Admin list
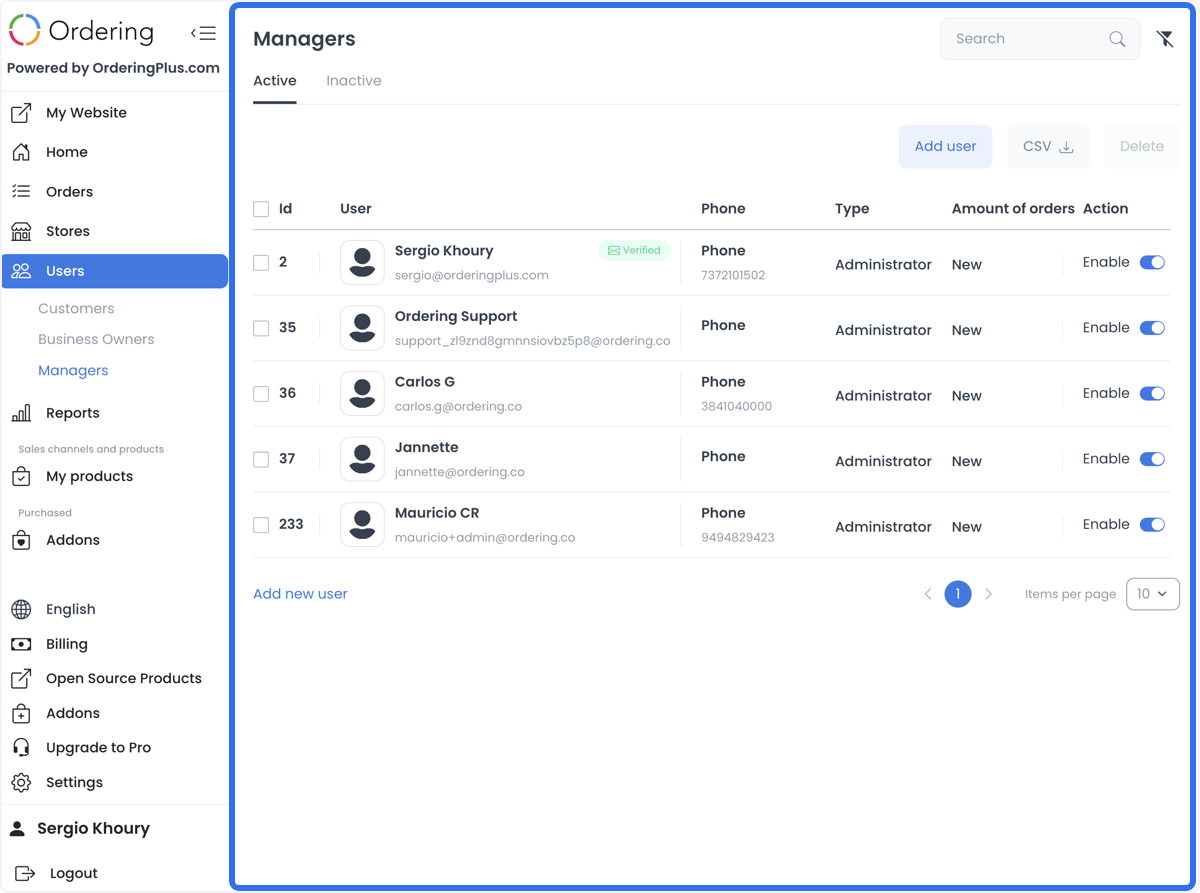
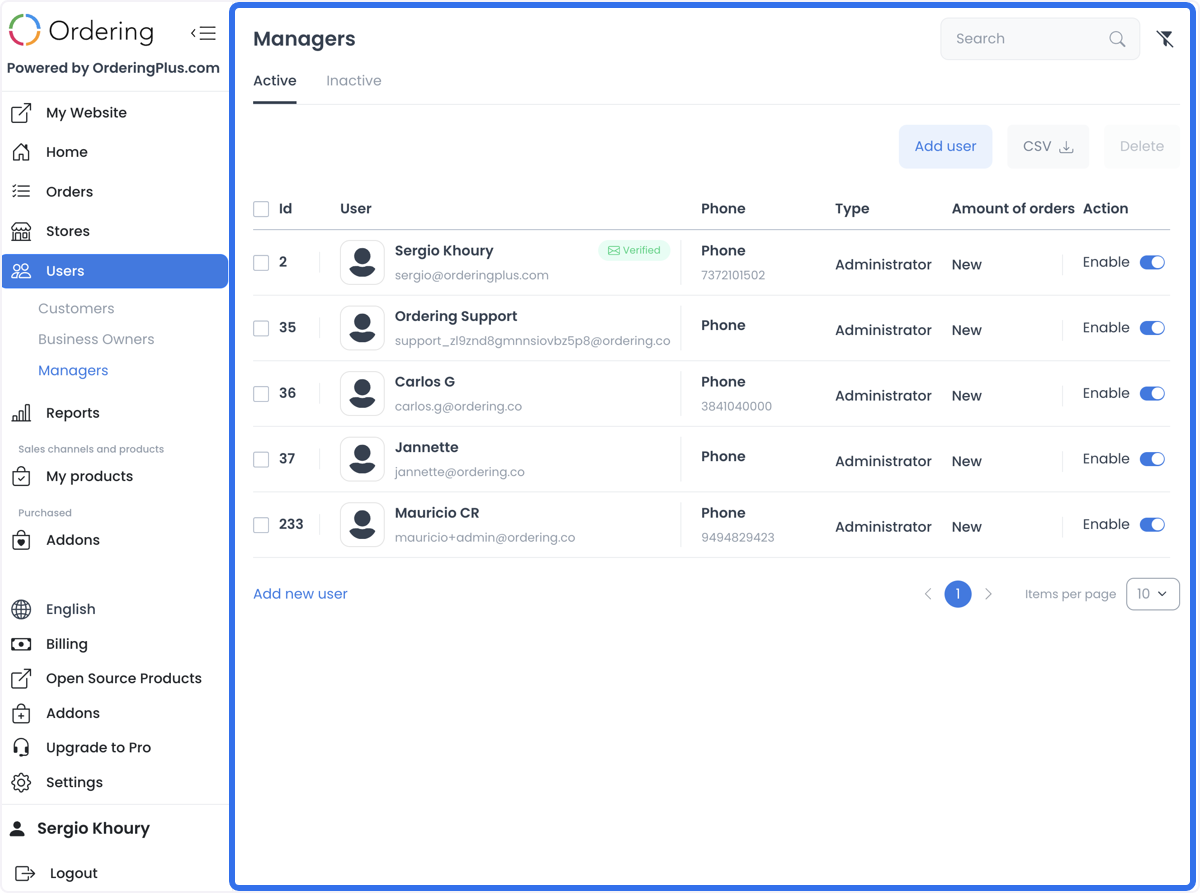
These screenshots are historical: the visible Dashboard label is Managers. This guide uses Admins as its documentation label for Administrator accounts; it does not rename the captured UI or establish a current Dashboard label.
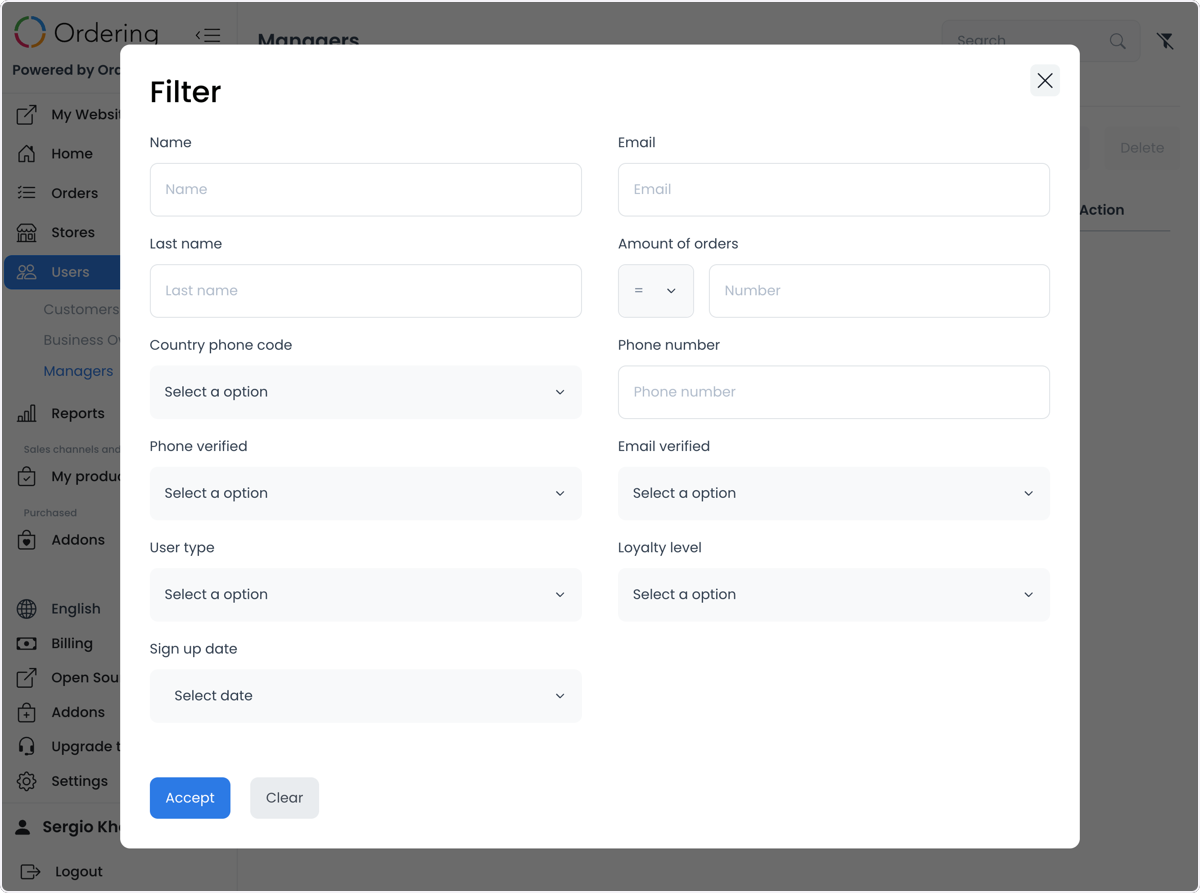
The historical Managers list can show administrator verification status, contact details, and active/inactive state. Use filters to locate a specific administrator, but treat returned identity and contact data as sensitive.
Filter and export deliberately
The list can filter administrators by available criteria such as verification or activity state. It can also expose a CSV export. Export only the minimum authorized data, protect the resulting file, and do not use a CSV export as a substitute for an access review.
Add an account
Add new user can begin an account-creation workflow. Confirm the intended role, identity, contact information, and authorization before saving. For the business-owner workflow, see Create or manage a Business owner.
Review an Admin profile
Selecting an Administrator can reveal profile information, verification status, and custom fields. A verified state is not a guarantee of identity, ongoing access, or trustworthiness; use the organization’s account-review process.
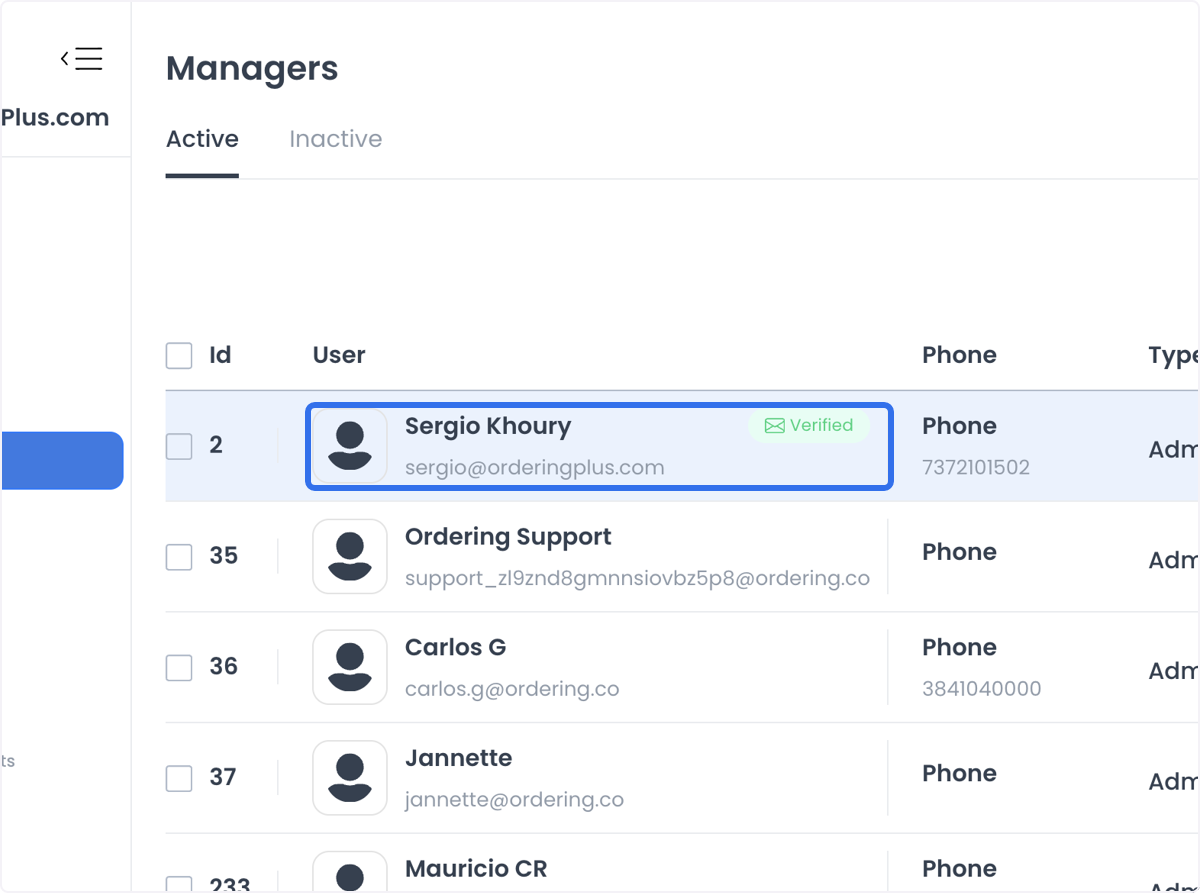
Verification and custom fields
The detail screen can present Verification Status and Custom fields. Review both only when you are authorized to see the account. Custom fields can contain operational or personal information and must be handled with the same privacy controls as the core profile.
Access scope
Administrator controls can affect users, orders, settings, and configuration, but a visible control does not establish that a particular action is permitted or completed. Follow the appropriate role and change-management workflow before using an access-changing or destructive action.